 The TechLens
Every time a customer signs up on a website, downloads an app, makes an online purchase or shares their contact details with a business, they are trusting that organisation with their personal information. But how carefully is that information being handled? Who has access to it? How long is it being stored? And what happens if it is exposed in a data breach?
These are no longer questions businesses can afford to overlook.
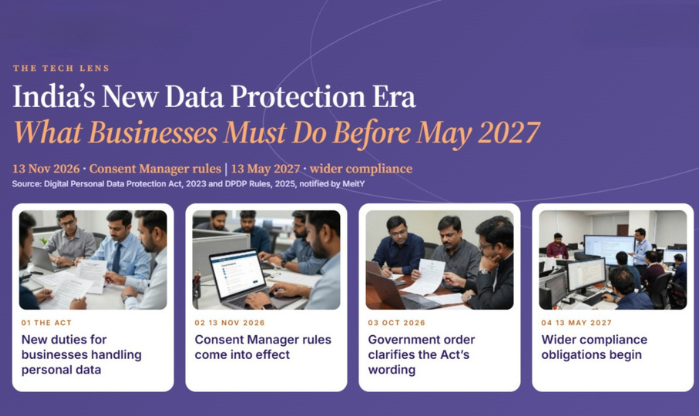
India is moving towards a more structured data protection environment under the Digital Personal Data Protection (DPDP) Act, 2023, and the DPDP Rules, 2025. With the framework following a phased implementation schedule, organisations have until 13 May 2027 to prepare for the wider substantive compliance requirements.
However, there is an important development much closer on the calendar. From 13 November 2026, Rule 4, which deals with the registration and obligations of Consent Managers, is scheduled to come into effect. An October 2026 government order has also clarified certain provisions of the original Act.
For business leaders, these developments are a reminder that data protection needs attention today, not just when the final deadline approaches.
Understanding What the DPDP Act Means for Everyday Business
Most organisations collect personal information as part of their daily operations. A retail company stores customer contact details, a bank processes financial information, a technology company manages user accounts, and an employer maintains employee records.
Over time, this information becomes part of the organisation’s business ecosystem. The challenge is ensuring that it is collected for legitimate purposes, handled responsibly and protected throughout its lifecycle.
That is where the DPDP Act comes in.
The legislation establishes responsibilities for organisations processing digital personal data, generally referred to as Data Fiduciaries. It also gives individuals greater control over their personal information, including rights relating to access, correction, erasure, grievance redressal and consent withdrawal, subject to the provisions of the Act.
In simple terms, businesses need to be more transparent about what information they collect, why they need it and how they use it.
The DPDP Rules, 2025, notified by MeitY, provide the operational framework for putting these responsibilities into practice.
November 2026: Why the Consent Manager Milestone Matters
One of the immediate developments is the commencement of Rule 4 on 13 November 2026.
But what exactly is a Consent Manager, and why should businesses pay attention?
Think about how often people agree to share their personal information when using digital services. In many cases, they may not revisit those permissions or know how to withdraw them later.
A Consent Manager is intended to make this process easier. It provides individuals with a platform to give, manage, review and withdraw consent for the processing of their personal data.
Under the DPDP framework, entities seeking to operate as Consent Managers must meet the prescribed eligibility and registration requirements. They will also be subject to specific obligations under Rule 4 and the First Schedule.
For businesses, this development is worth monitoring because consent management could become an increasingly important part of how digital services interact with customers.
However, there is an important distinction: the November 2026 milestone applies to the Consent Manager framework. It is not the general compliance deadline for every organisation.
October 2026: What the Government’s Clarification Means
Another development businesses should be aware of is the Digital Personal Data Protection (Removal of Difficulties) Order, 2026, issued in October.
The order addresses two provisions in the original Act.
One clarification relates to Section 9(1), which deals with processing children’s personal data and the personal data of persons with disabilities who have lawful guardians. The other concerns Section 10(2)(c)(ii), clarifying the reference to a periodic data audit in the provisions applicable to Significant Data Fiduciaries.
For most businesses, the takeaway is not that an entirely new compliance regime has been introduced. Rather, the government has clarified specific statutory wording as the implementation process moves forward.
Organisations should ensure that their legal and compliance teams refer to the updated provisions while preparing their internal policies.
Five Practical Steps Businesses Can Start Taking Now
Understanding a regulation is one thing. Preparing an organisation to follow it is another. The good news is that businesses do not need to wait until 2027 to begin making meaningful changes.
Here are five areas worth reviewing.
1. Find out what personal data your business actually holds
Start with a simple question: what information are we collecting, and where does it go? Customer databases, employee records, website registrations, marketing lists and vendor systems are all worth examining. Businesses should understand who accesses this information and whether it is shared with external service providers.
2. Make consent easier to understand
Have you ever signed up for a service without fully understanding its privacy terms? Your customers may be doing the same. Review website forms, mobile applications and registration processes to ensure that privacy notices clearly explain what information is collected and why. Consent requests should be clear and specific rather than hidden inside lengthy terms and conditions.
3. Look beyond basic cybersecurity
Installing security software is not enough. Organisations should examine access permissions, encryption, monitoring, backups and security testing. Employees should only have access to the information they need to perform their responsibilities.
4. Stop retaining information without a clear reason
Many organisations continue storing customer and employee information long after it is needed. This can create unnecessary exposure. Establish appropriate retention periods and deletion procedures, while accounting for applicable legal and regulatory requirements.
5. Know what happens when something goes wrong
A data breach can quickly become a business problem, affecting customer confidence and organisational reputation. Companies should establish clear escalation procedures, identify who is responsible for responding and prepare to meet the applicable notification requirements for affected individuals and the Data Protection Board.
Why Business Leaders Need to Be Involved
Data protection is often viewed as an IT or legal department responsibility. In reality, it touches almost every part of an organisation.
Marketing teams work with customer information. HR departments manage employee records. Sales teams maintain prospect databases. Technology teams oversee applications and infrastructure. Even external vendors may have access to information that belongs to the organisation’s customers.
This is why compliance needs to be a shared responsibility.
CXOs should encourage teams to work together, review vendor arrangements, invest in appropriate safeguards and make employees aware of their responsibilities. Smaller businesses and startups should pay attention too, as the Act can apply to organisations of different sizes that process digital personal data.
Certain additional requirements apply to organisations designated as Significant Data Fiduciaries.
The Road Ahead: Preparing Before May 2027
India’s DPDP framework is not simply another regulation that businesses can address by updating a privacy policy. It calls for a closer look at how personal information moves through an organisation, from the moment it is collected to the point it is deleted.
The November 2026 Consent Manager milestone and the October clarification order show that implementation is progressing. With the wider substantive obligations scheduled to commence on 13 May 2027, businesses have an opportunity to prepare in a planned and practical manner.
Ultimately, customers should not have to wonder whether their personal information is being handled responsibly. That confidence needs to come from the way businesses operate every day.
For Indian organisations, preparing for DPDP compliance is no longer just a legal exercise. It is an important part of earning and maintaining customer trust.
For more latest developments in technology, business and digital transformation subscribe to The Tech Lens.